Monday Morning, Five Figures: Anatomy of a Weekend Phone Fraud
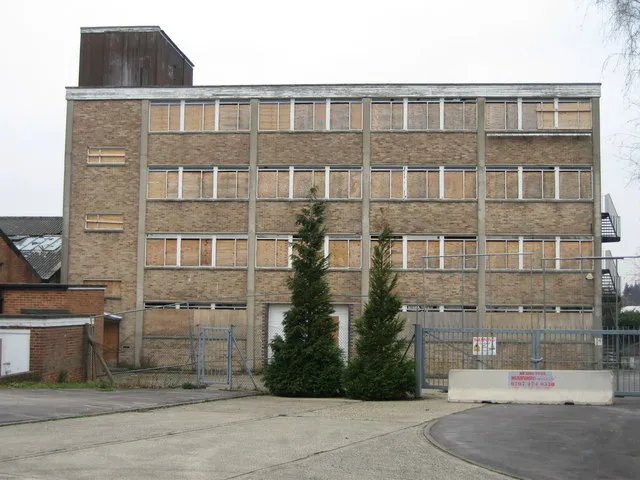
Photo: Sebastian Ballard, CC BY-SA 2.0, via Wikimedia Commons
The emails arrived at 8.40 on Monday morning. Not from a customer, and not from the bank, but from the finance director of a twelve-person marketing agency just outside Nottingham, forwarding a phone bill that should have read £180 and instead read £14,237. By lunchtime the firm's VoIP account had been suspended by its provider, its outbound calling was frozen, and the question on everyone's lips was the same one that follows every case like this: how does a phone system empty a company's account over a single weekend without anyone noticing?
The answer, in almost every instance, is that nobody was watching. Toll fraud against small and medium-sized businesses is not a sophisticated heist. It is a patient, automated process that exploits the hours between Friday evening and Monday morning, when offices are empty and call records go unread.
How the Weekend Unfolds
Reconstructing the Nottingham firm's call logs with its provider revealed a now-familiar sequence. At 11.52pm on Friday, someone accessed the web portal for the company's phone system using credentials that had, until three weeks earlier, been printed on a welcome email still sitting in a departed employee's inbox.
The first change was small. A single entry in the auto-attendant — the recorded menu that greets callers — was altered so that one extension forwarded to an overseas number. Then, in the early hours of Saturday, call-forwarding rules on two dormant extensions were pointed at premium-rate destinations in Eastern Europe and West Africa.
From that point, the fraud ran itself. Automated diallers called the hijacked extensions continuously, each call routed onward to numbers controlled by the fraudsters. Because the traffic was generated from within the account itself, nothing looked unusual from the outside. By Sunday night, the system had logged over 9,000 calls. The providers' fraud systems flagged the volume, but the alert went to the account's registered email address — the same compromised inbox.
Why Small Firms Are the Preferred Target
There is a persistent belief that fraudsters only pursue large enterprises. The opposite is true. SMEs typically run phone systems with default passwords, unmonitored portals and no after-hours calling restrictions. A twelve-person agency will rarely have anyone accountable for telecoms security, and providers' credit limits — often set generously for business accounts — allow days of fraudulent calling before any hard stop.
The economics favour the criminal. International premium-rate numbers can command several pounds per minute, with the terminating operator paying a share back to the number's owner. Every minute your system spends connected is a minute of revenue for them, billed to you.
The Detection Checklist
Any business can run the following checks in under an hour, and should do so quarterly:
- Review forwarding rules on every extension, particularly those assigned to leavers or rarely used meeting rooms. Anything forwarding outside the UK should have a documented business reason.
- Audit the auto-attendant and IVR menus. Confirm every option routes where it should, and that no temporary or seasonal diversion survives from a previous campaign.
- Check portal user accounts. Remove access for former staff and confirm no accounts use default or shared passwords. Enable two-factor authentication if the provider offers it.
- Examine weekend and overnight call logs. Even a handful of international calls made at 3am on a Sunday warrants investigation.
- Confirm your spend cap. Many UK providers apply a credit limit only on request; if yours is set to the maximum 'just in case', it offers no protection.
The Safeguards to Demand From Your Provider
The Nottingham firm's recovery — a partial goodwill refund and a hardened account — began with a phone call it should never have needed to make. When reviewing your own arrangement, ask your provider these questions directly:
- Can international and premium-rate outbound calling be disabled by default, and re-enabled only for specific destinations?
- Is there an account-level spending cap that triggers an automatic bar, rather than an email alert?
- Are fraud alerts sent by SMS to a named individual as well as by email?
- Can call-forwarding to external numbers be restricted outside business hours?
- What is the provider's written policy on liability when account credentials are compromised?
Providers vary considerably in what they offer as standard. Some apply aggressive real-time anomaly detection at no extra cost; others treat fraud protection as an optional add-on. The difference is rarely visible until the moment it matters.
The Cost of Looking Away
The agency in question survived, but only just. The disputed charges were eventually settled at roughly a third of the original bill after a lengthy complaint, the frozen outbound lines cost it two days of client work, and the finance director now reviews call logs every Monday morning — a habit that, she notes wryly, would have cost her ten minutes a week for the previous three years.
Phone fraud of this kind does not announce itself. It arrives as a line item, quietly and completely, while everyone is at home. The firms that avoid it are not the ones with the most expensive security; they are the ones who asked, before the weekend, who was watching the phones.